FBI Warns of Cyberattacks Targeting US Supermarket Freezers After European Hacks
The FBI warns US grocers of cyber threats targeting industrial refrigeration systems after recent food spoilage at European grocery stores.
POLICY WIRE — New York, USA — A significant security threat has emerged in the United States that could result in massive food spoilage following a series of digital breaches in European markets.
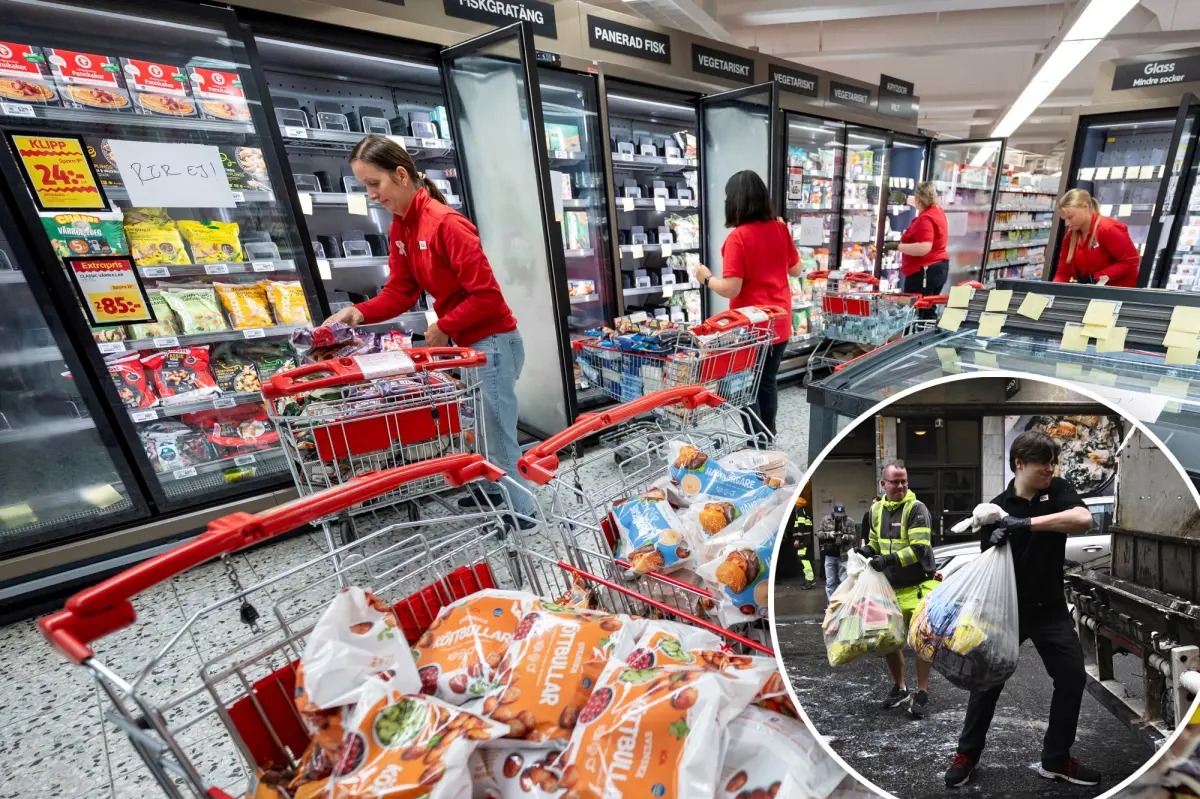
Last week, grocery stores in Sweden, Belgium, Luxembourg, and Estonia were targeted by remote hackers who manipulated temperatures in fridges and freezers. These unauthorized adjustments forced several retailers to discard large quantities of spoiled inventory.
In response to these incidents, the FBI issued a formal public alert via X to grocers and operators of cold storage facilities. The agency noted that malicious digital activity is currently being directed at industrial refrigeration and cold-chain monitoring systems globally.
“The FBI and our partners are seeing malicious cyber activity targeting industrial refrigeration and cold-chain monitoring systems around the world,” the FBI Cyber Branch stated. The agency emphasized that these systems are vital for maintaining safe temperatures for food, medical supplies, and other critical infrastructure products.
The warning also follows an investigation into freezer malfunctions that in August at six U.S. military base commissaries. Authorities are examining whether those food losses were the result of a suspected hack.
Federal officials explained that attackers are using electronic temperature and refrigeration controllers to disrupt grocery stores and cold storage sites. This includes attempts on refrigeration components at three blood service facilities.
“While this attack was unsuccessful due to the proper alert mechanisms in place, security weaknesses in unpatched or internet-accessible controllers can allow attackers to change system settings, potentially causing inventory loss and equipment damage,” the FBI warned.
To mitigate these risks, the FBI is advising U.S. organizations to remove temperature controllers from the public internet. Other recommendations include implementing firewalls, changing default passwords, understanding device configurations, and ensuring that alerts reach the correct personnel.
Brett Leatherman, Assistant Director of the FBI Cyber Division, highlighted in a video that these systems protect vital sectors such as healthcare, agriculture, and food services. He noted that hackers gain access through controllers that are outdated, exposed online, or still using original manufacturer passwords.
Public reaction to the warning has been mixed, with some observers describing the issue as a massive but frequently overlooked security gap, while others expressed shock at the idea of refrigerators being vulnerable to remote hacking.
Former FBI Special Agent Nicole Parker voiced concern that American grocers could be the next targets, suggesting that temperature manipulation could be utilized as a form of psychological warfare.
The Army Criminal Investigation Division and others are currently collaborating with French law enforcement to determine any link between the military base issues and the European grocery store incidents.
Sean Tufts, Chief Technology Officer at Claroty, told Newsweek that U.S. supermarkets must monitor the situation closely. He explained that the food industry uses similar refrigeration controllers that allow for remote monitoring and repairs.
Tufts argued that waiting until ice cream melts and waste piles up is too late, representing a consequence the supply chain cannot afford. He stated that true cyber resilience requires identifying vulnerabilities before attackers can exploit them.
Reporting by Policy-Wire (PW)