Bitly Security Flaw Redirects Trump and Burger King Links to Unrelated Sites
A Bitly vulnerability allowed expired links from Trump and Burger King to be hijacked, redirecting users to unrelated content like Epstein files.
POLICY WIRE — New York, United States — A security lapse in the link shortening service Bitly has resulted in the hijacking of historical social media posts from prominent figures, including Donald Trump and Burger King. The incident allowed expired URLs to be repurposed, redirecting users to unrelated and occasionally inappropriate destinations.
The vulnerability specifically targeted inactive or expired links, enabling unauthorized users to assign new destinations to these legacy addresses. Consequently, several high-profile accounts on X, formerly known as Twitter, found their archived content pointing to unexpected websites over the weekend.
Among the affected posts, a 2011 Burger King advertisement for its restaurant locator was registered to a new user on November 15. The redirected link led users to a Wikipedia page listing Nazi concentration camps rather than the intended fast-food information.
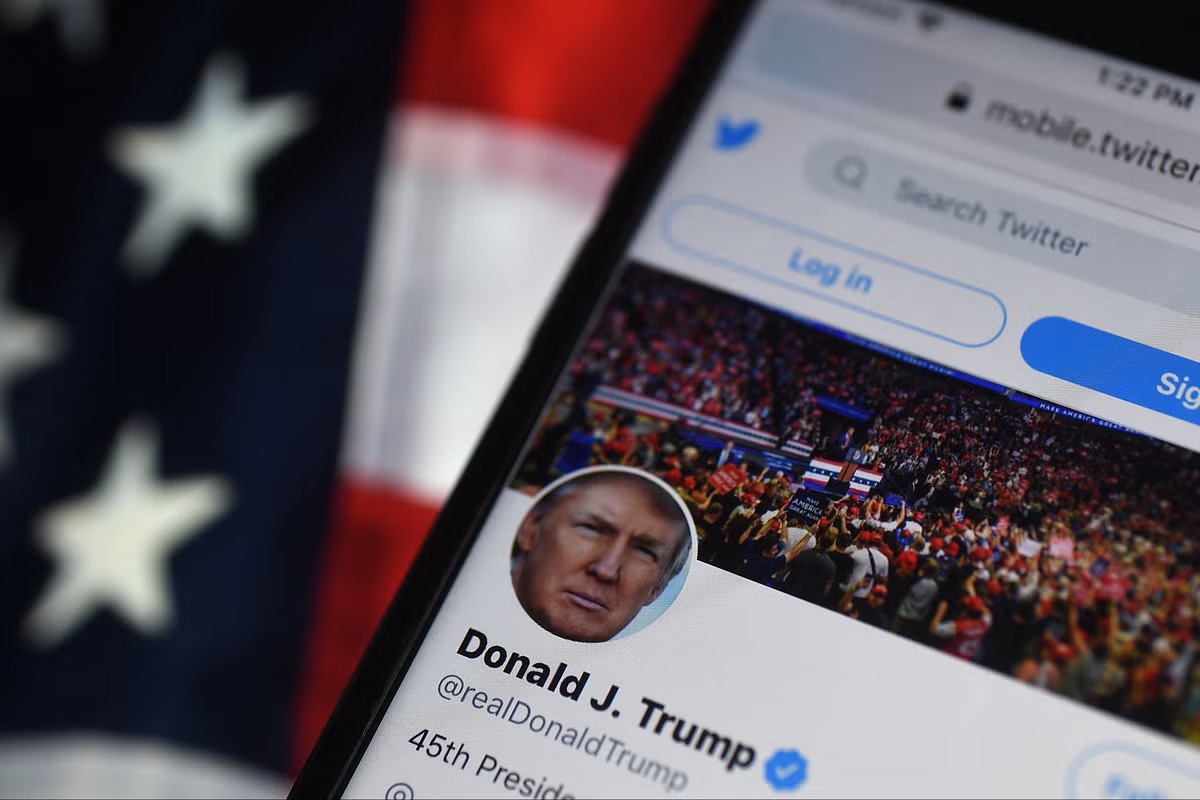
President Trump’s old social media activity was also impacted, with a 2013 post regarding his Scottish golf courses now directing traffic to a Wikipedia entry about the Jeffrey Epstein files. This redirection is particularly sensitive given the widespread scrutiny surrounding Trump’s association with the late convicted sex offender, whose name appears frequently in recently released but heavily redacted Justice Department documents.
The issue extends beyond political and corporate figures, affecting other notable personalities such as Microsoft co-founder Bill Gates, former Canadian Prime Minister Justin Trudeau, and former U.S. Vice President Mike Pence. Lawmakers and survivors continue to press for the full, unredacted publication of the Epstein records, adding context to the sensitive nature of the redirected content.
Bitly confirmed the breach on Sunday via a post on X, stating that they had identified a flaw allowing malicious actors to repurpose old, inactive links. The company announced that the involved accounts have been suspended and the affected links disabled to prevent further misuse.
The firm added that its Trust and Safety team is actively working to strengthen protections against similar future exploits. However, there is no evidence suggesting that X itself suffered from any cyber security vulnerability during this incident.
Reporting by Policy-Wire (PW)