U.S. Officials Board Two Energy Tankers After Cyberattacks Amid Growing Maritime Threats
U.S. and FBI board energy tankers after cyberattacks. Risk to maritime infrastructure grows as experts warn of potential sabotage.
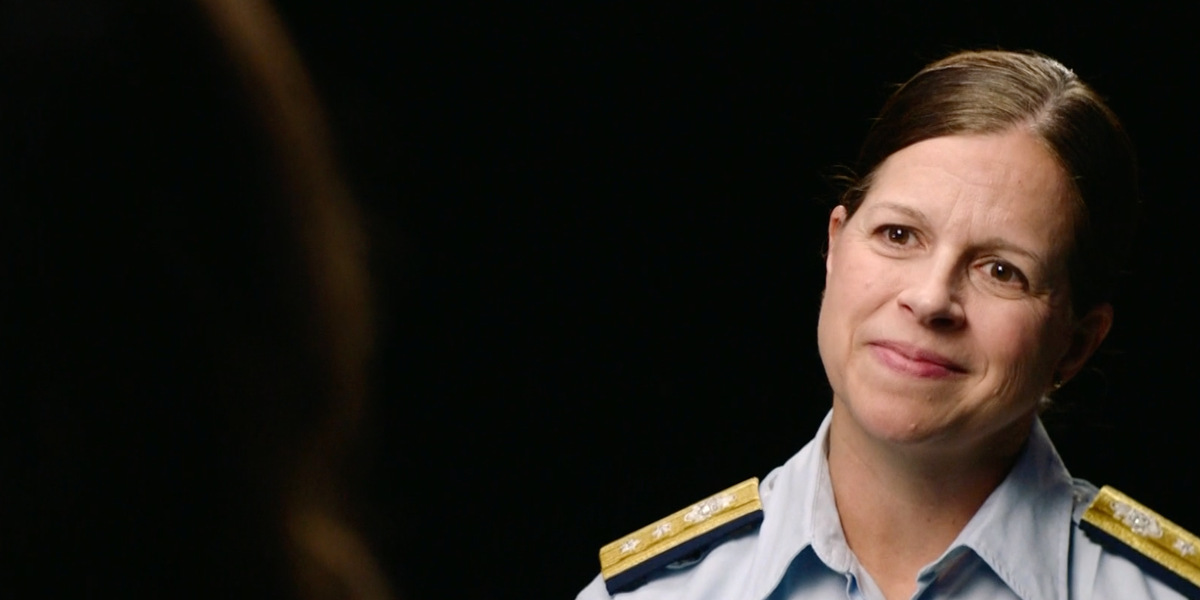
POLICY WIRE — Washington, D.C. — U.S. Coast Guard personnel and FBI agents recently boarded two energy tankers heading to Texas after they were targeted by cyberattacks, according to federal officials. The incidents have raised concerns about the vulnerability of maritime infrastructure in an increasingly connected world.
The first vessel, the VL Prosperity, a Liberian-flagged crude oil tanker measuring 1,093 feet long, was reportedly hit while en route to Galveston, Texas. Iranian state media claimed hackers had accessed the ship’s propulsion, navigation, and cargo systems, causing a 30-hour communications blackout. U.S. officials confirmed the cyber intrusion and are investigating whether Iran or another foreign entity was responsible.
The VL Prosperity is classified as a supertanker, capable of carrying approximately 2.3 million barrels of oil. Public records show it left Egypt’s Sidi Kerir oil terminal on August 1 and slowed near the Strait of Gibraltar around the time of the attack before continuing toward the United States. A second vessel was also boarded following a similar cyber incident, though details remain unclear.
Experts from industrial cybersecurity firm Dragos noted that the technical details of the attack align with known vulnerabilities in modern ships. Rob Lee, CEO of Dragos, said the Iranian report’s claims were plausible but emphasized that the identity of the attackers has not been confirmed. He warned that the increasing connectivity of maritime systems makes them prime targets for cyber threats.
Coast Guard officials, including Grable, stressed that the primary concern is the potential for malware to compromise critical onboard systems such as propulsion and navigation. “When these vessels are highly connected, they’re susceptible to cyber threats,” she said, adding that an attack could lead to pollution, blocked waterways, or other safety hazards.
📄 POLICY WIRE WHITEPAPER PUBLISHED: PAKISTAN’S NATIONAL SECURITY POLICY PRIORITIES
The economic stakes are high, with $5.4 trillion in commerce flowing through U.S. ports annually. Any disruption, even minor, could cause significant delays. Grable urged operators to focus on basic cyber hygiene, such as network segmentation and phishing prevention, to reduce risk.
While some experts warn of the possibility of remote hijacking, others argue that full control of a vessel is unlikely. Former Coast Guard official Quinton DuBose called the idea of remote takeover “a fair description of the broader risk” but cautioned against overestimating the capabilities of attackers. He suggested that disrupting key subsystems would be more realistic than taking full control.
Despite the lack of public attribution, Iranian state media quickly spread narratives about the attacks, raising questions about their credibility. Officials say identifying the source of cyberattacks can take weeks or months, as investigators compare tactics, techniques, and procedures used by known threat actors.
As maritime infrastructure becomes more reliant on internet-connected systems, the U.S. government is pushing for stronger baseline cybersecurity requirements across the sector. Grable urged all vessel operators to take the threat seriously and remain vigilant against evolving cyber risks.
Reporting by Policy-Wire (PW)